Security and risk arrive as noise: audit findings, pen-test reports, supplier questionnaires, exceptions in email, spreadsheets with _FINAL_v3 in the name. frinc turns those signals into one ordered record that leadership can read, question and track, as at today, not reconstructed for the meeting.
Quietly in pilot with Australian organisations. Built in Sydney.
From signals to one record
Before: signals as they arrive
CPS234_evidence_FINAL_v3.xlsxPTEST-002 report.pdfAfter: one record, as at today sample data
AC-021MFA enforcement, proof on file for the insurerverified todayBK-004Backup immutability, evidence stale94 daysST-002Pen-test findings, 3 open, 1 accepted with exception3 openSM-011Supplier assurance, annual reviewverified 9dRK-017Ransomware, residual above appetite, owner namedabove appetiteAssessments, findings, risks, exceptions, actions, evidence and suppliers stay connected instead of collected.
A control proven for one framework reads across the others it maps to, without re-testing it for every auditor.
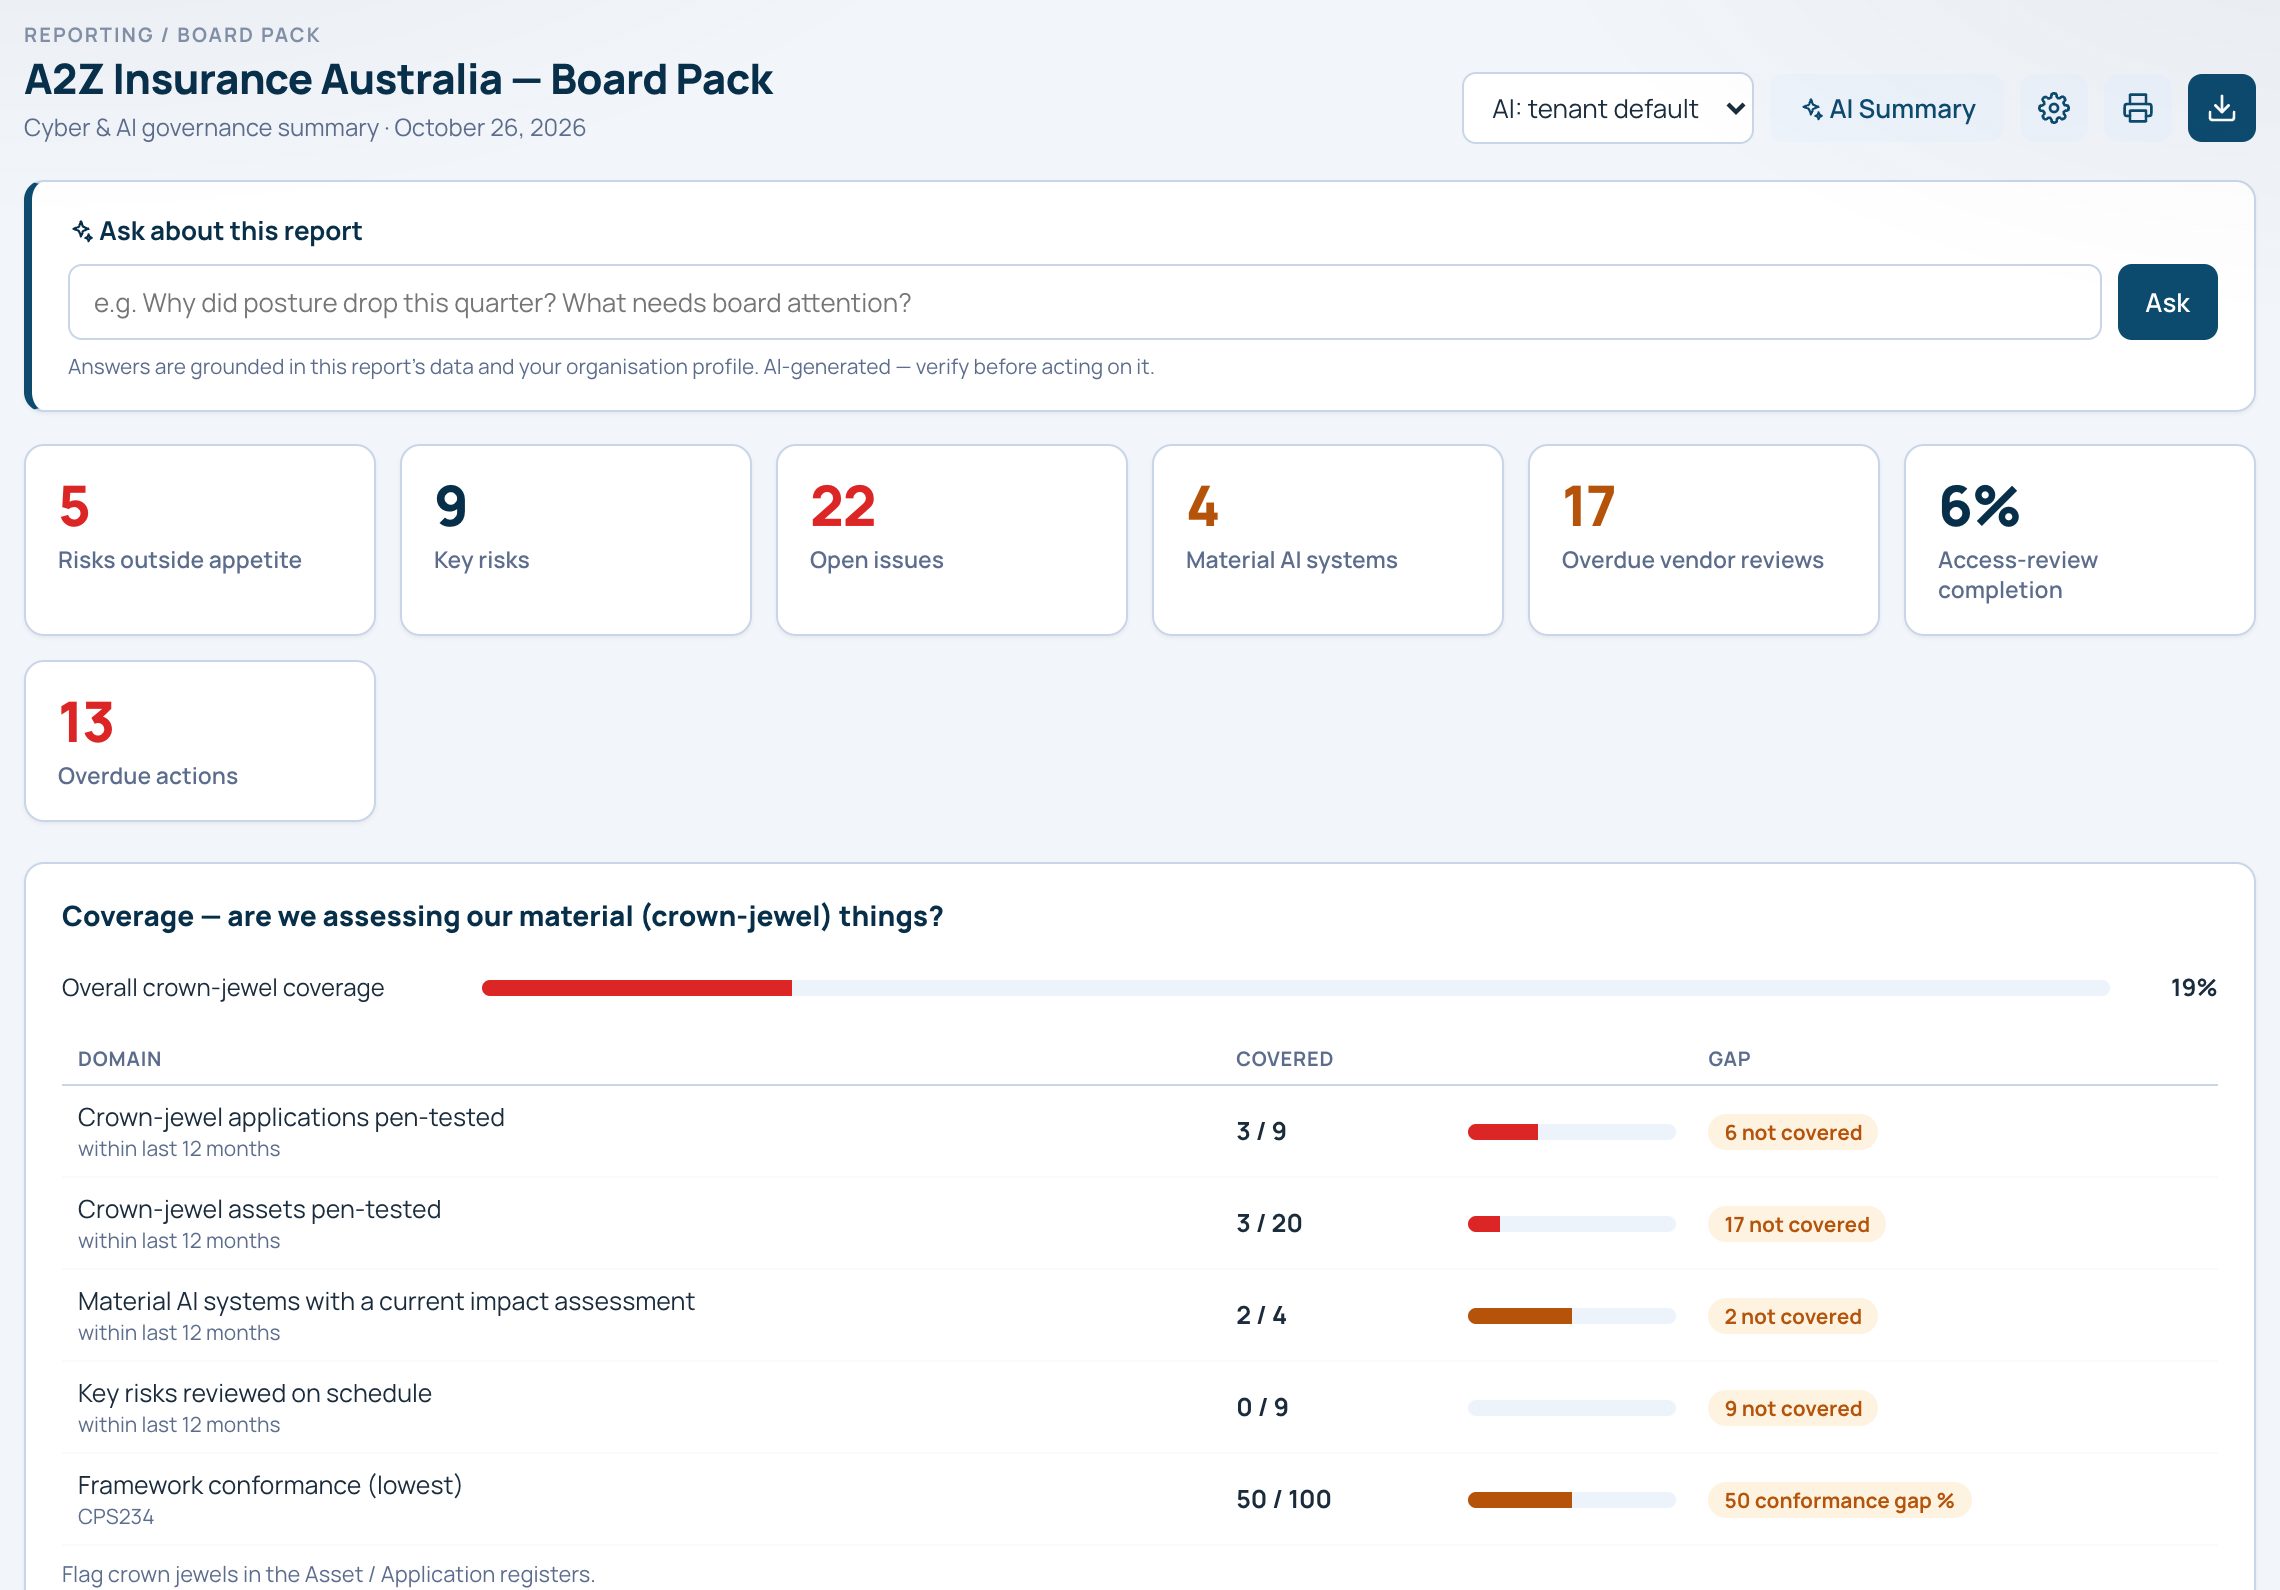
The board answer is the live record, not a slide assembled the night before. Ask it a question and it answers from your records.
The platform
Each part below is a module in the same product, sharing one set of owners, controls and evidence.
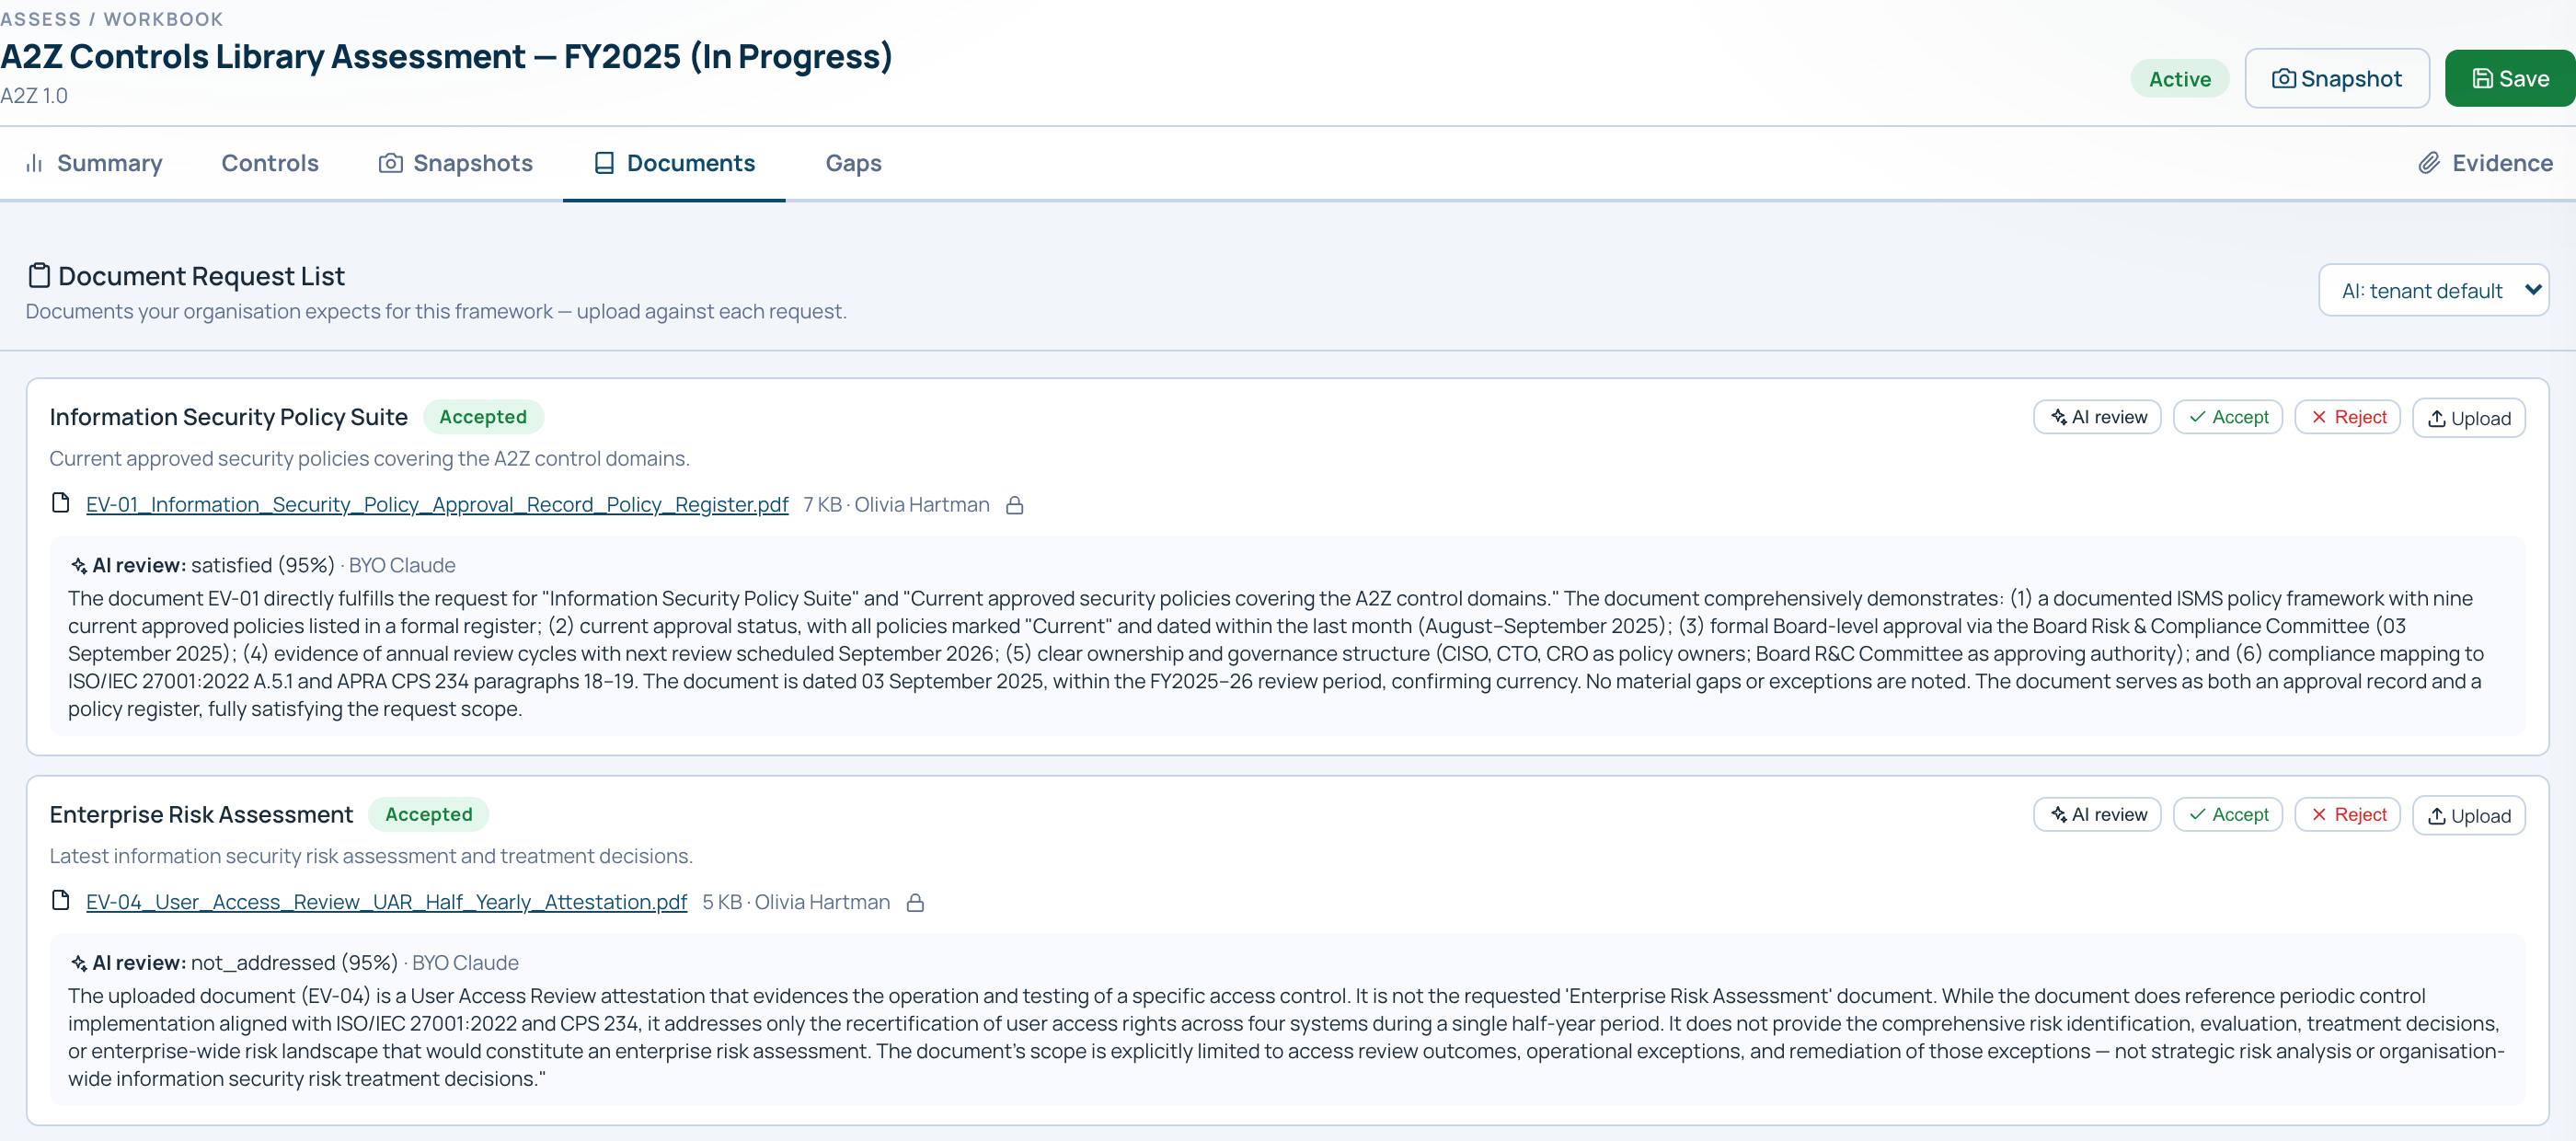
Assess against every framework you are held to in one workbook, and collect the documents each framework needs against every assessment.

AS-01Security assessmentsFW-01Framework libraryDR-01Document requestsRP-01Assessment reportsFrameworks in the library from day one
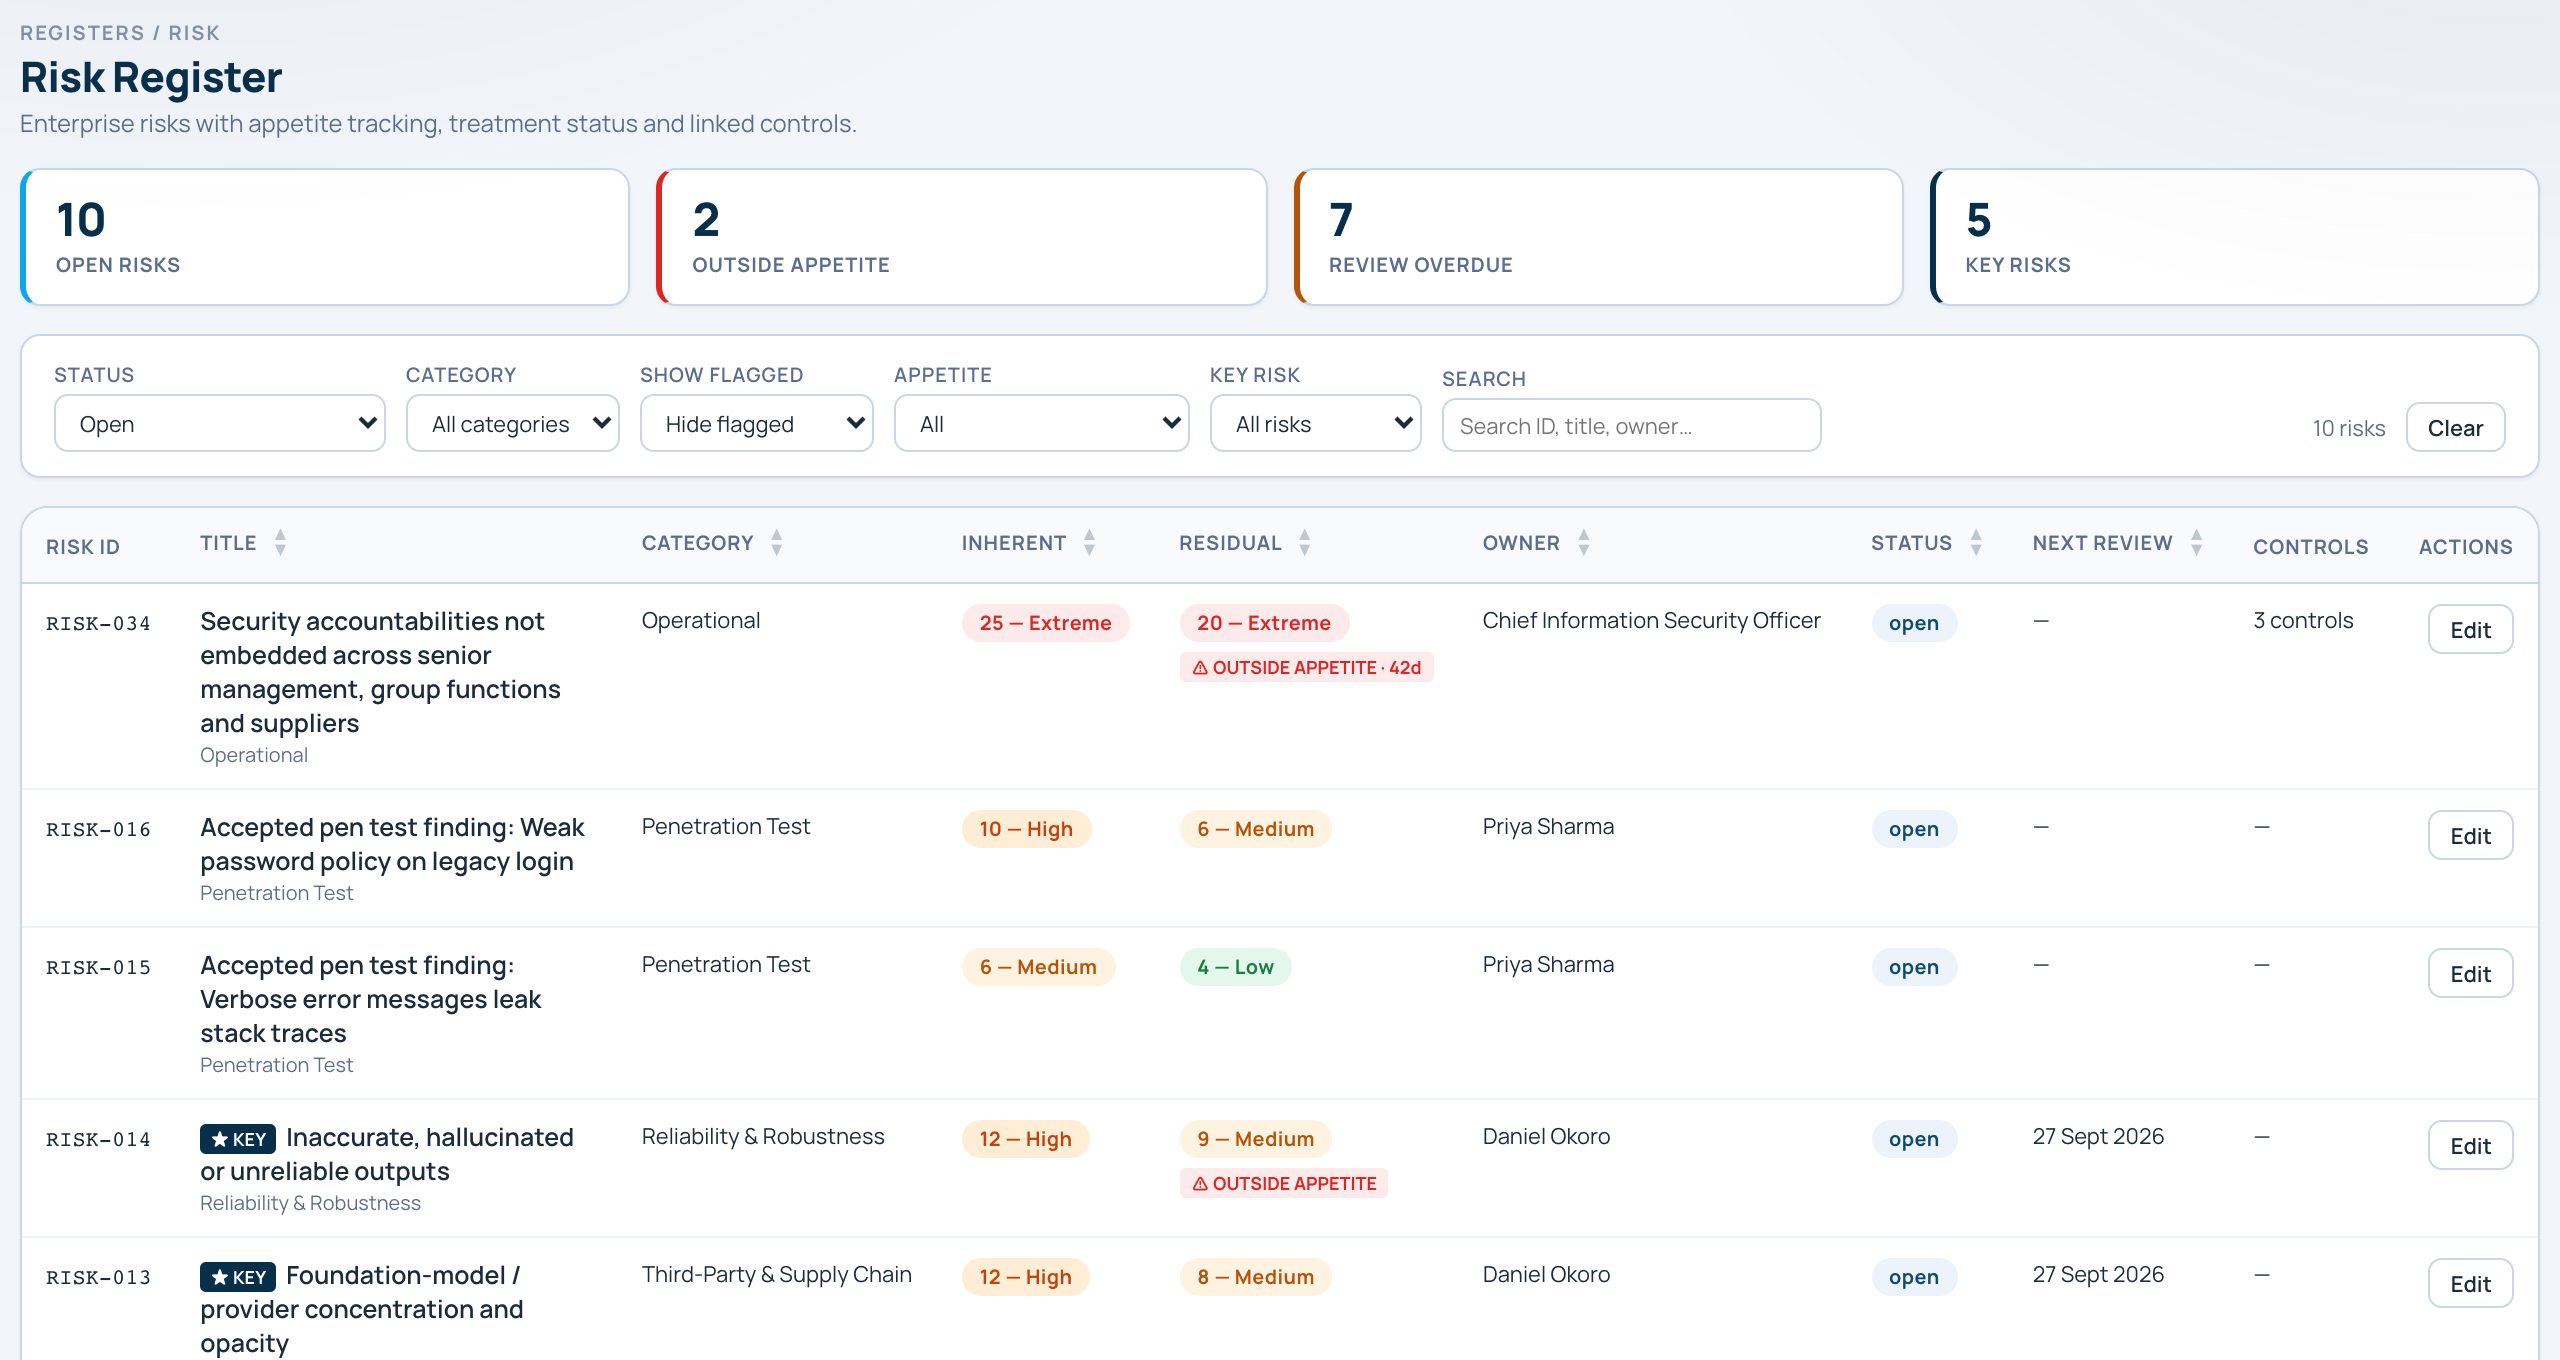
Risks, issues, exceptions, actions, assets, applications, suppliers and access reviews in one product, each record linked to the controls and people behind it.

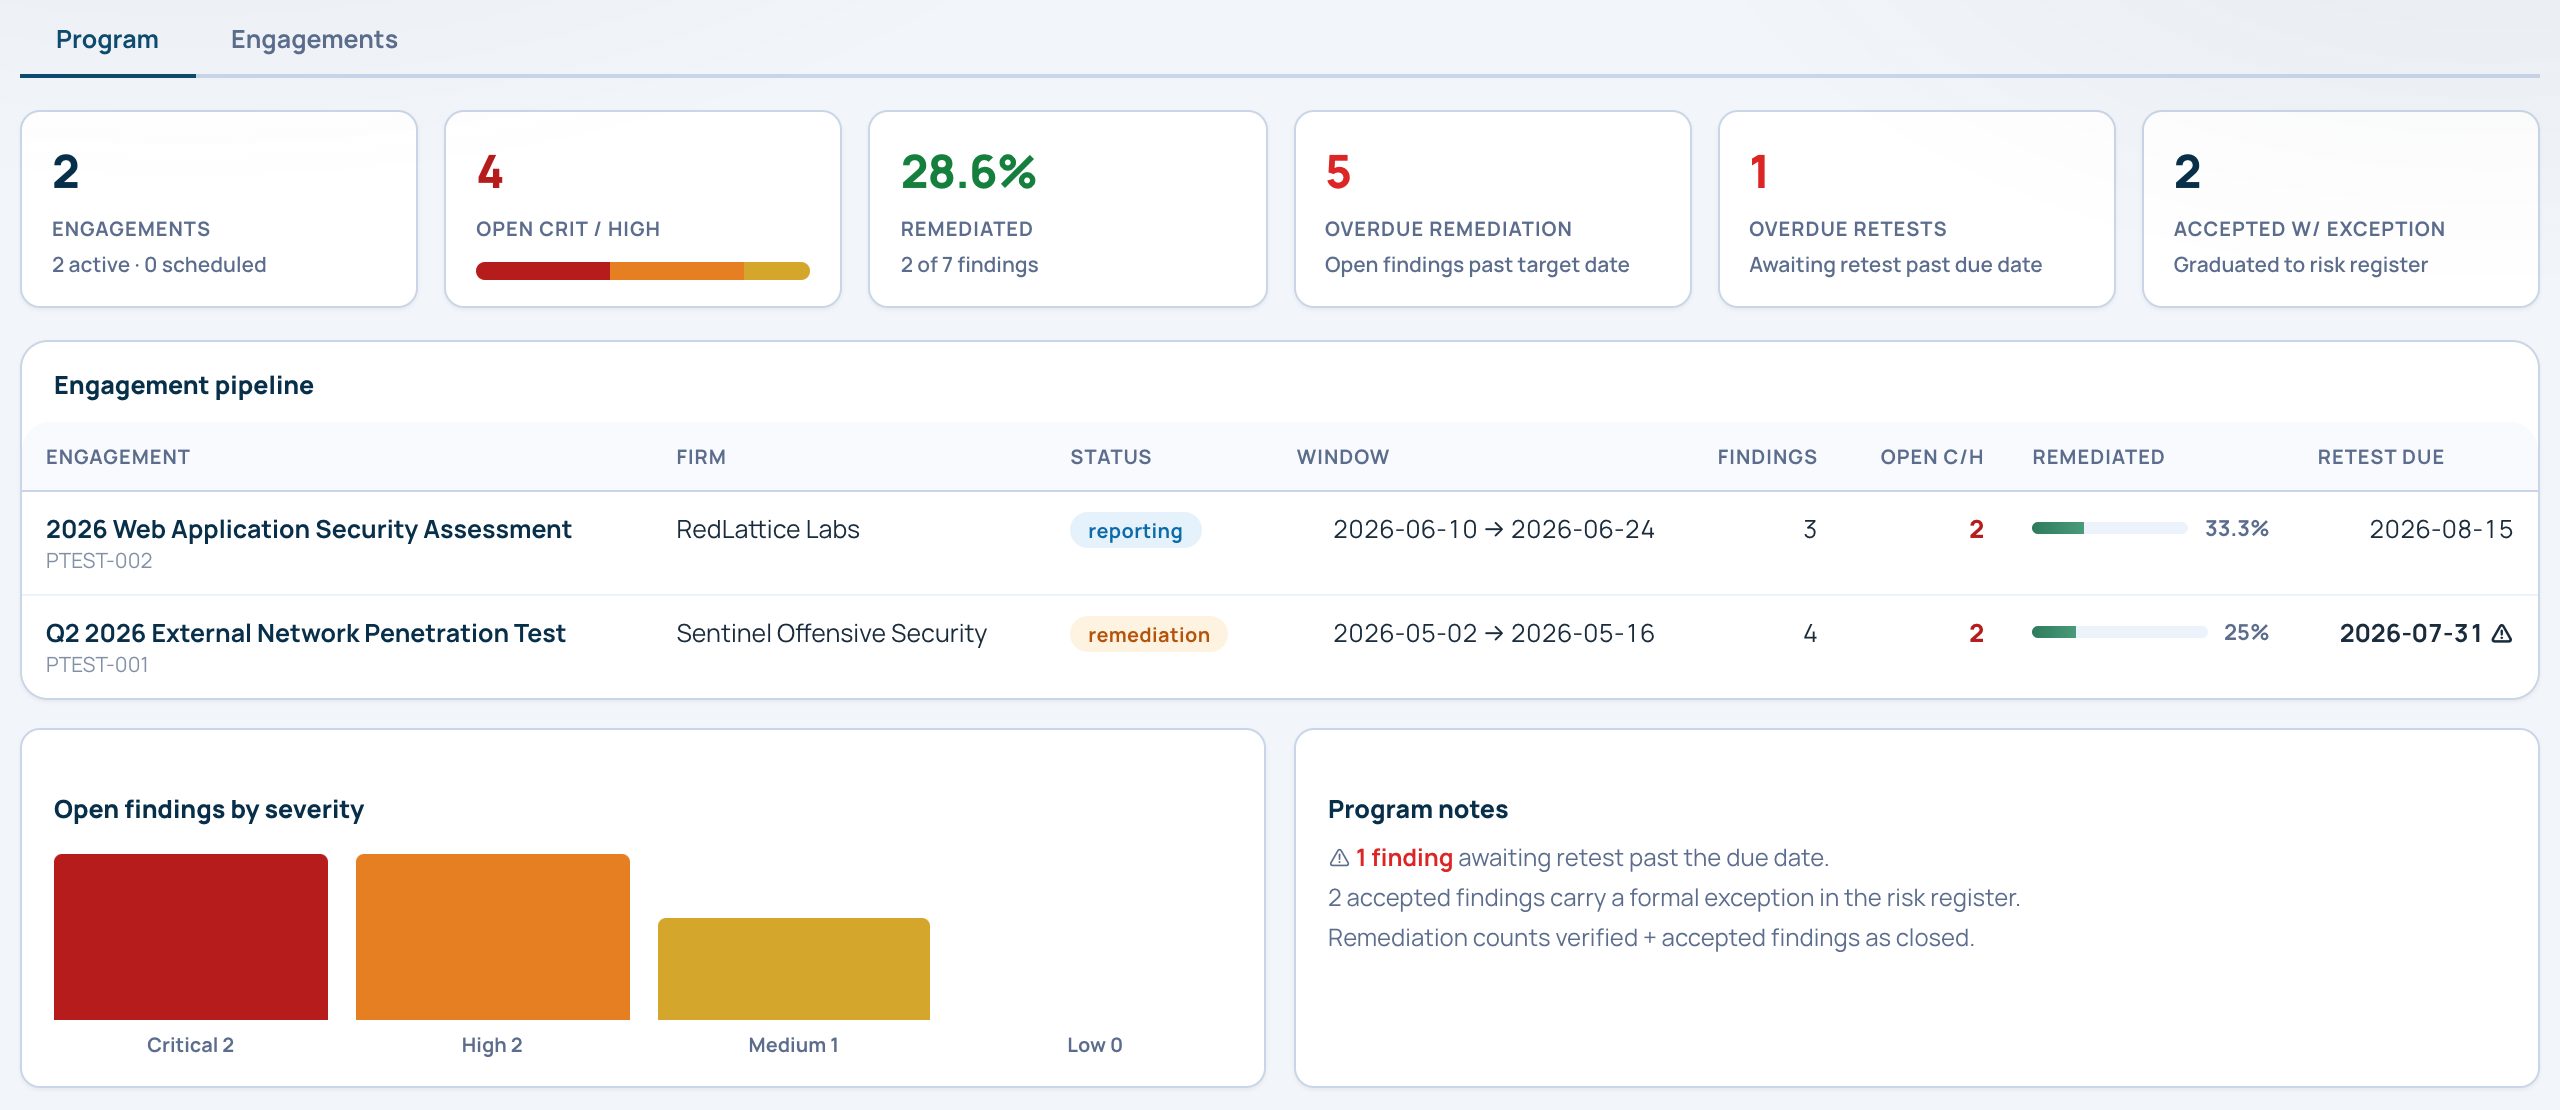
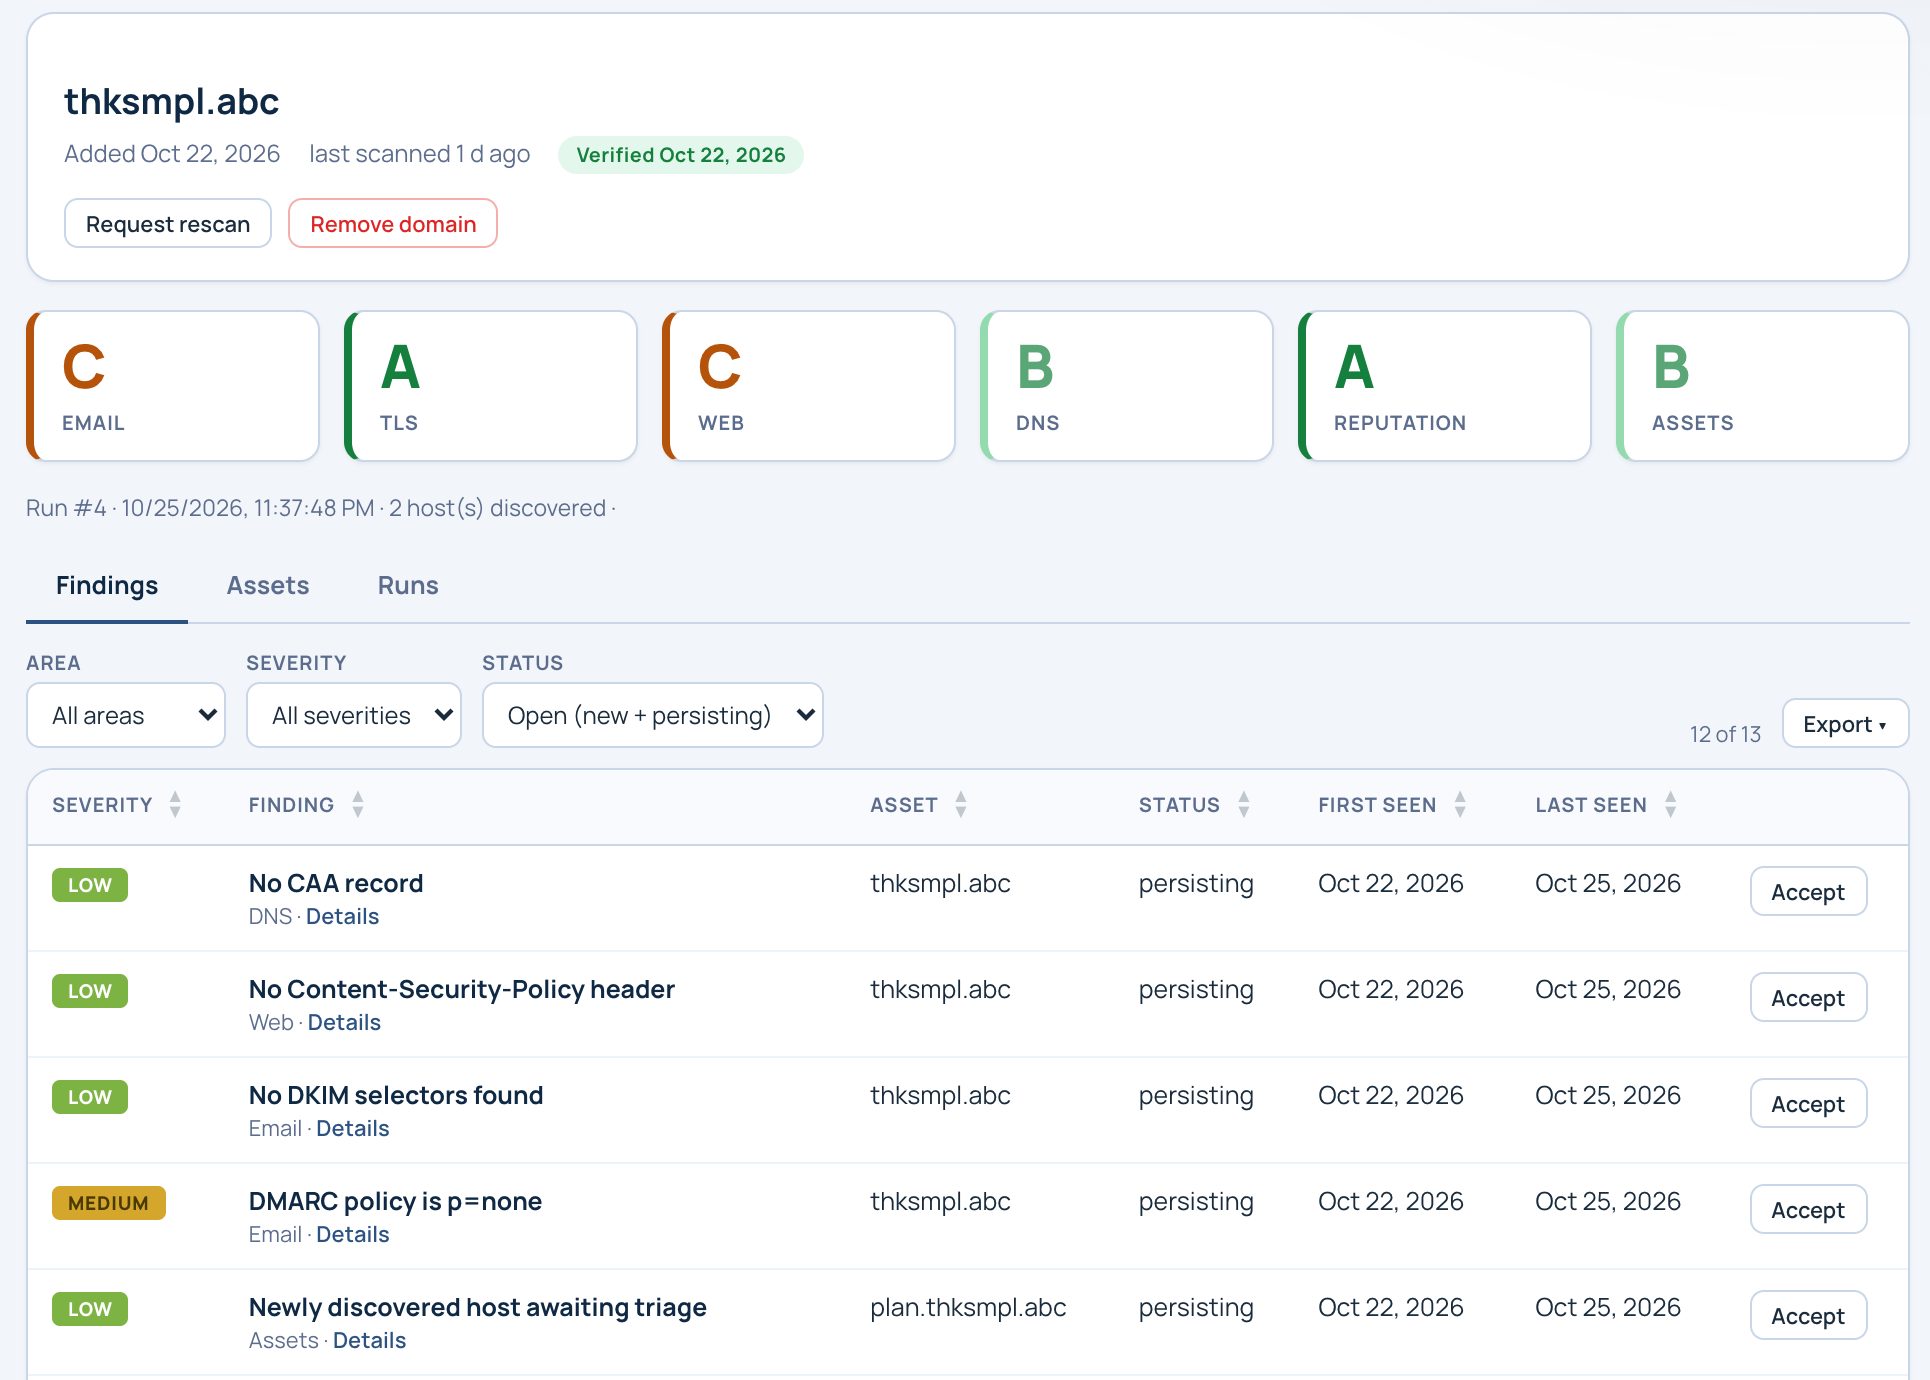
RR-01RisksIS-01IssuesEX-01ExceptionsAP-01Actions & projectsAT-01AssetsAI-01ApplicationsTP-01Third partiesAR-01Access reviewsExposure management in one place: what your testers found, what the internet can see of you, and what attackers are talking about this week. Every finding lands in the same risk register as everything else.


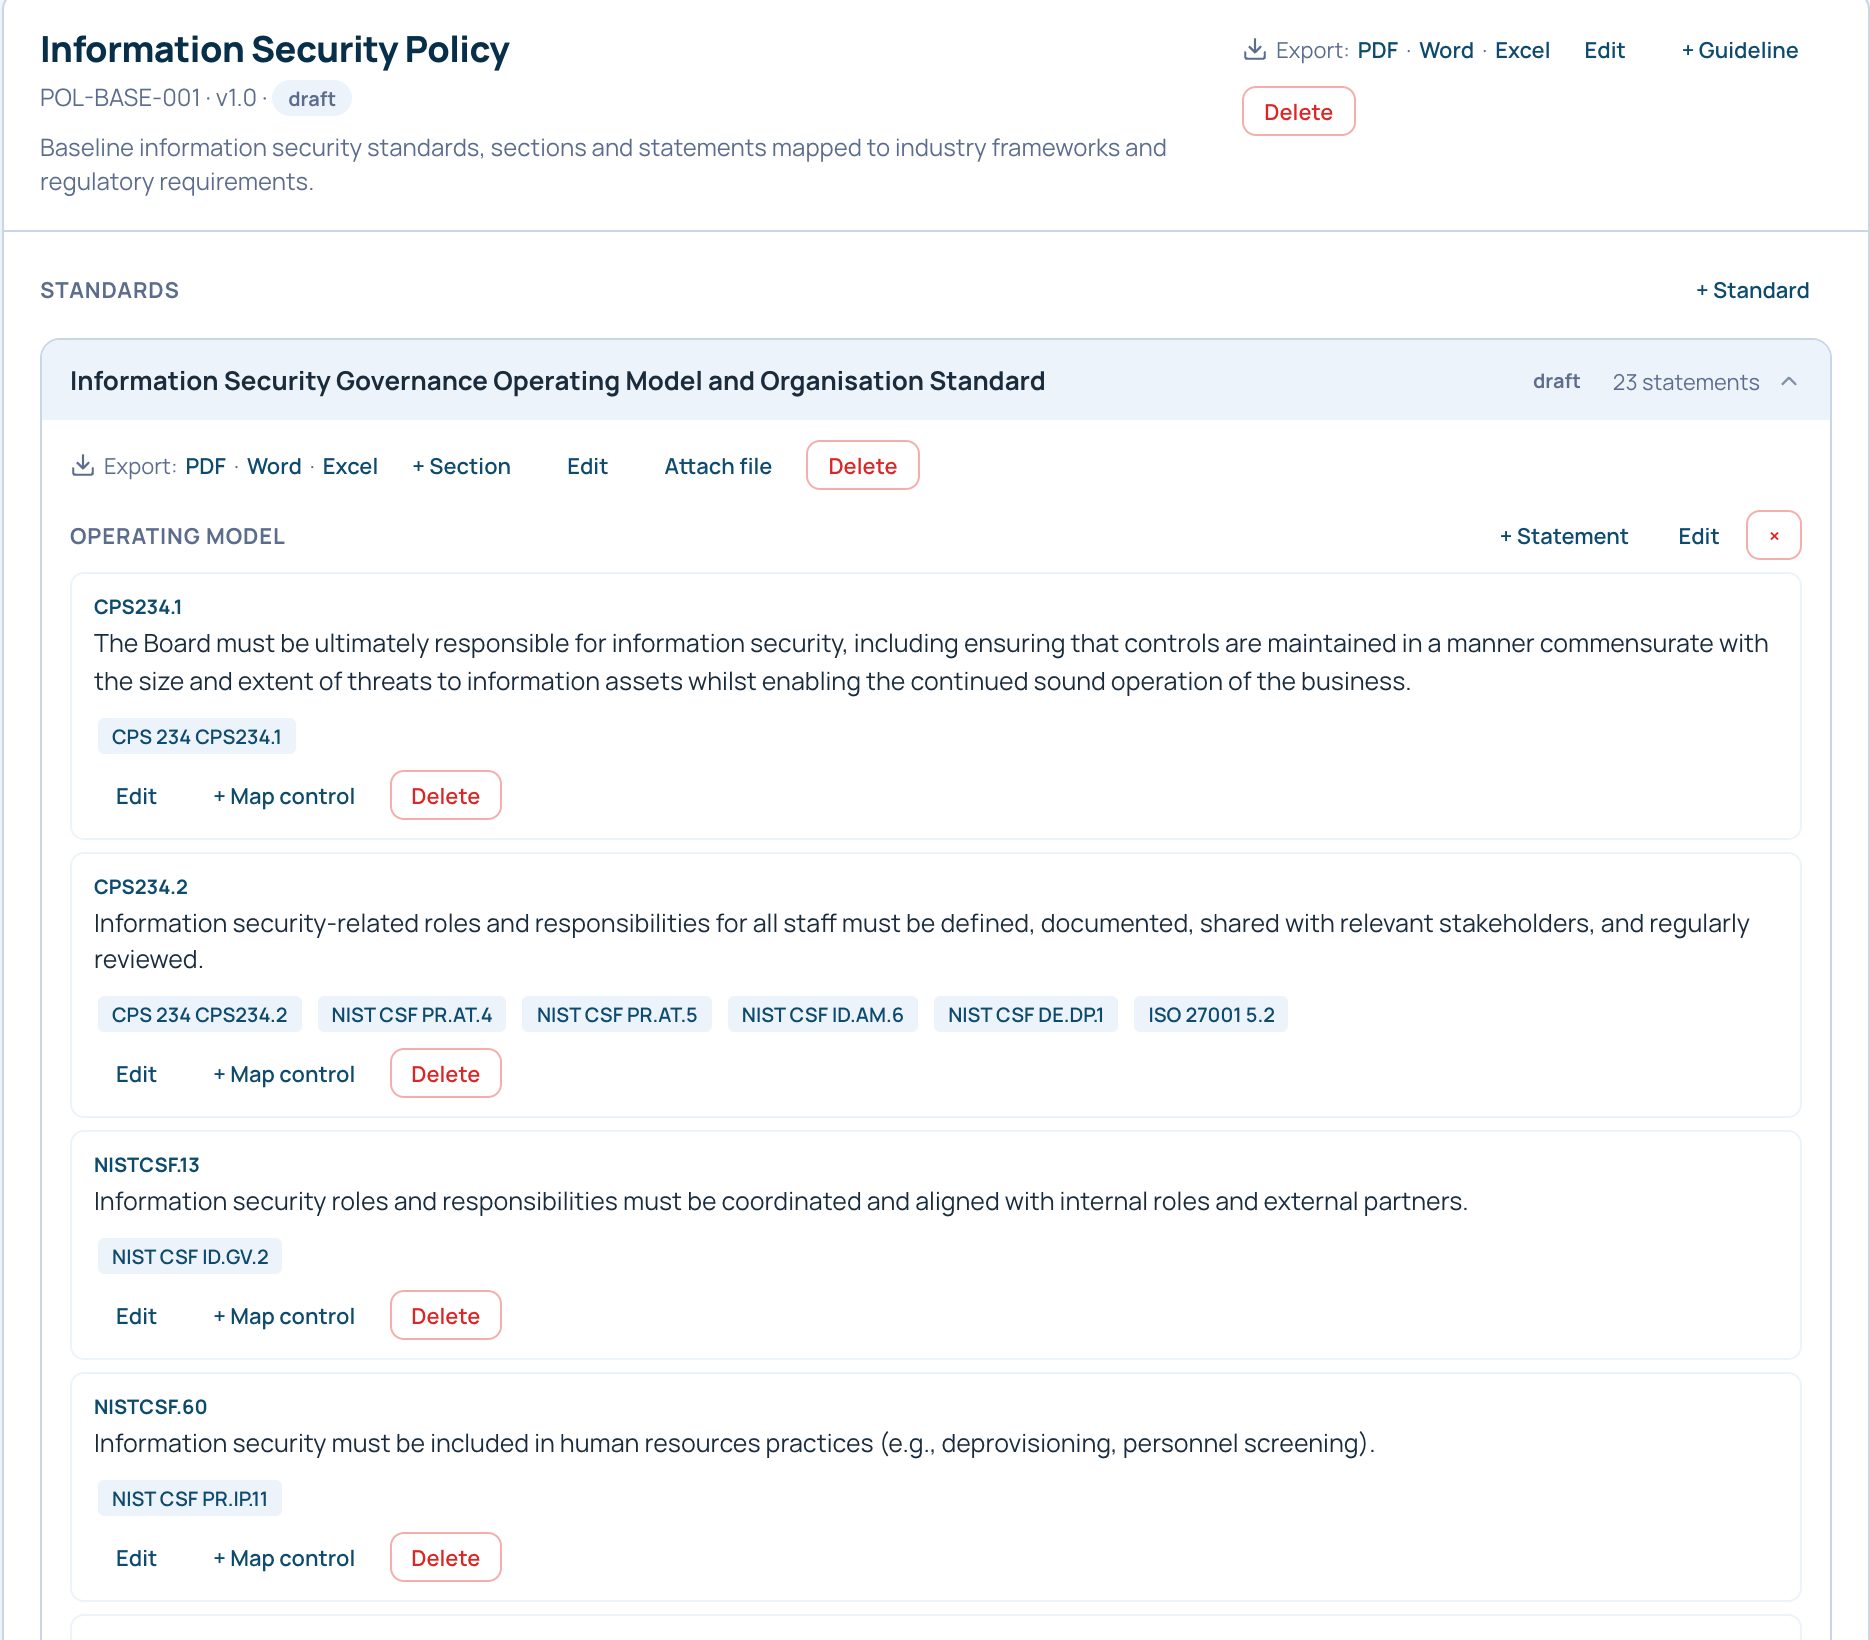
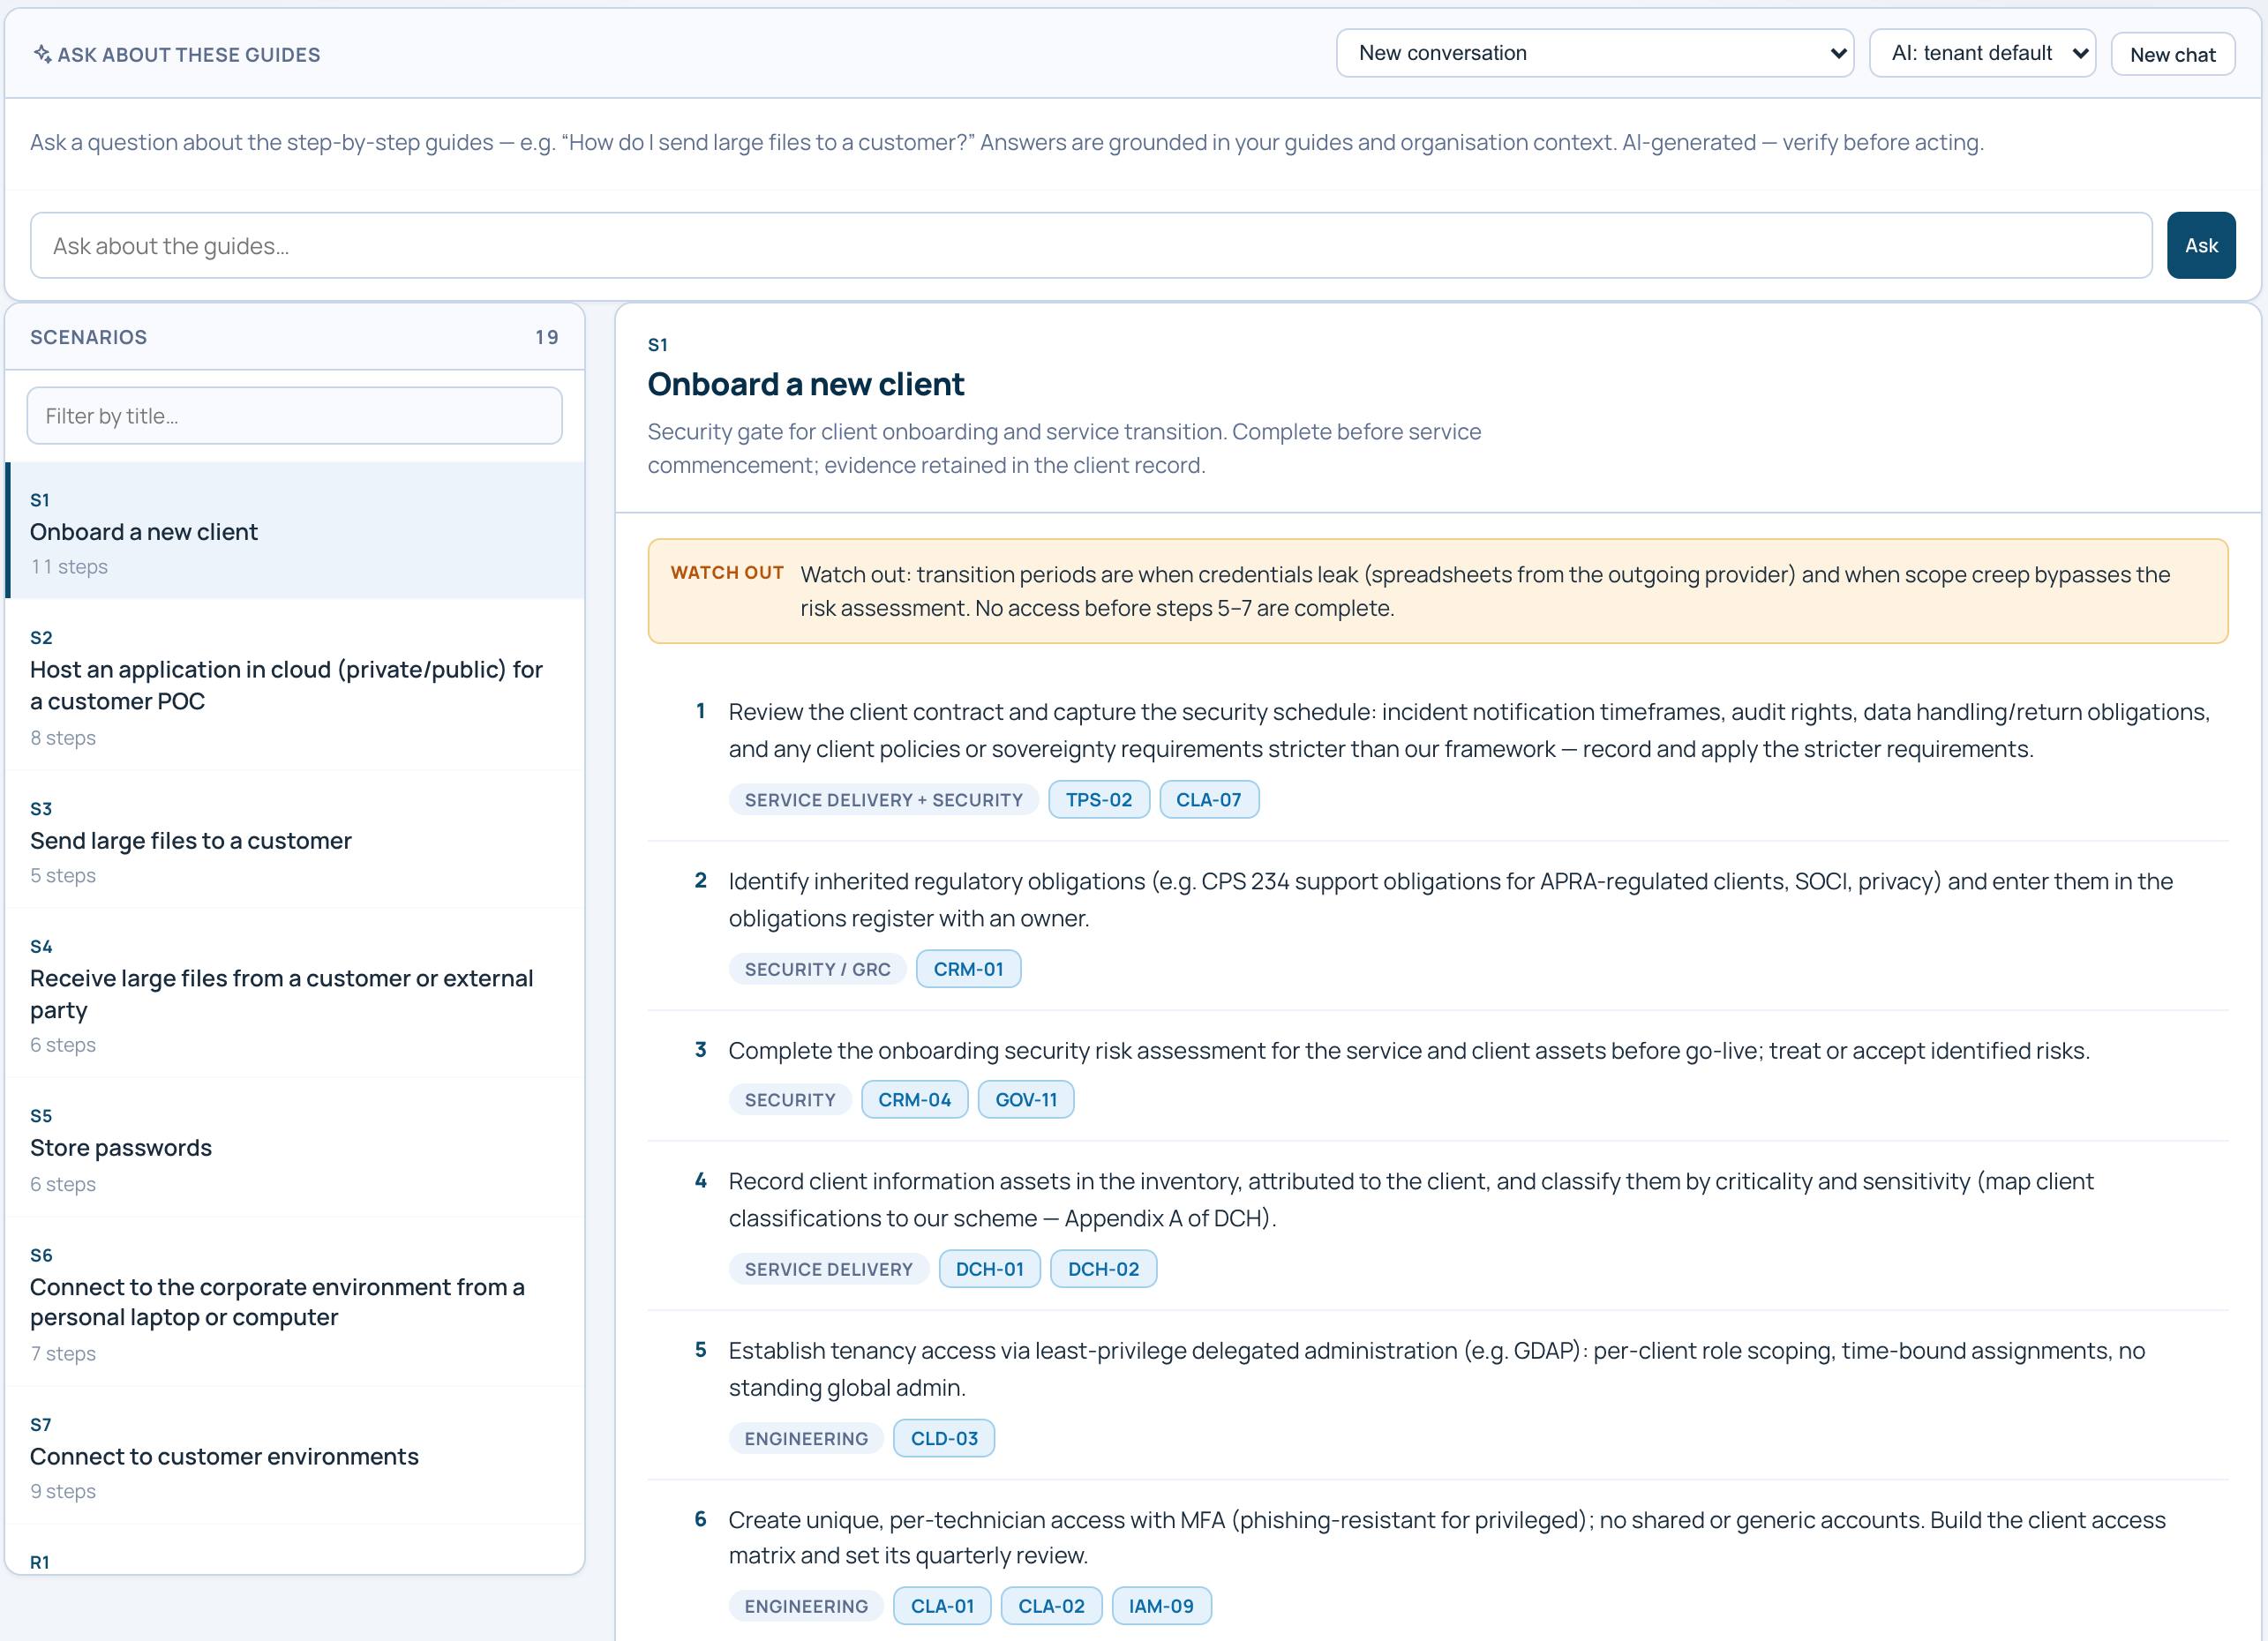
PT-01Pen test trackingEP-01External postureTI-01Threat intelligenceKeep the policy library, the how-to guides that put it into practice and the AI systems you are accountable for in one place.


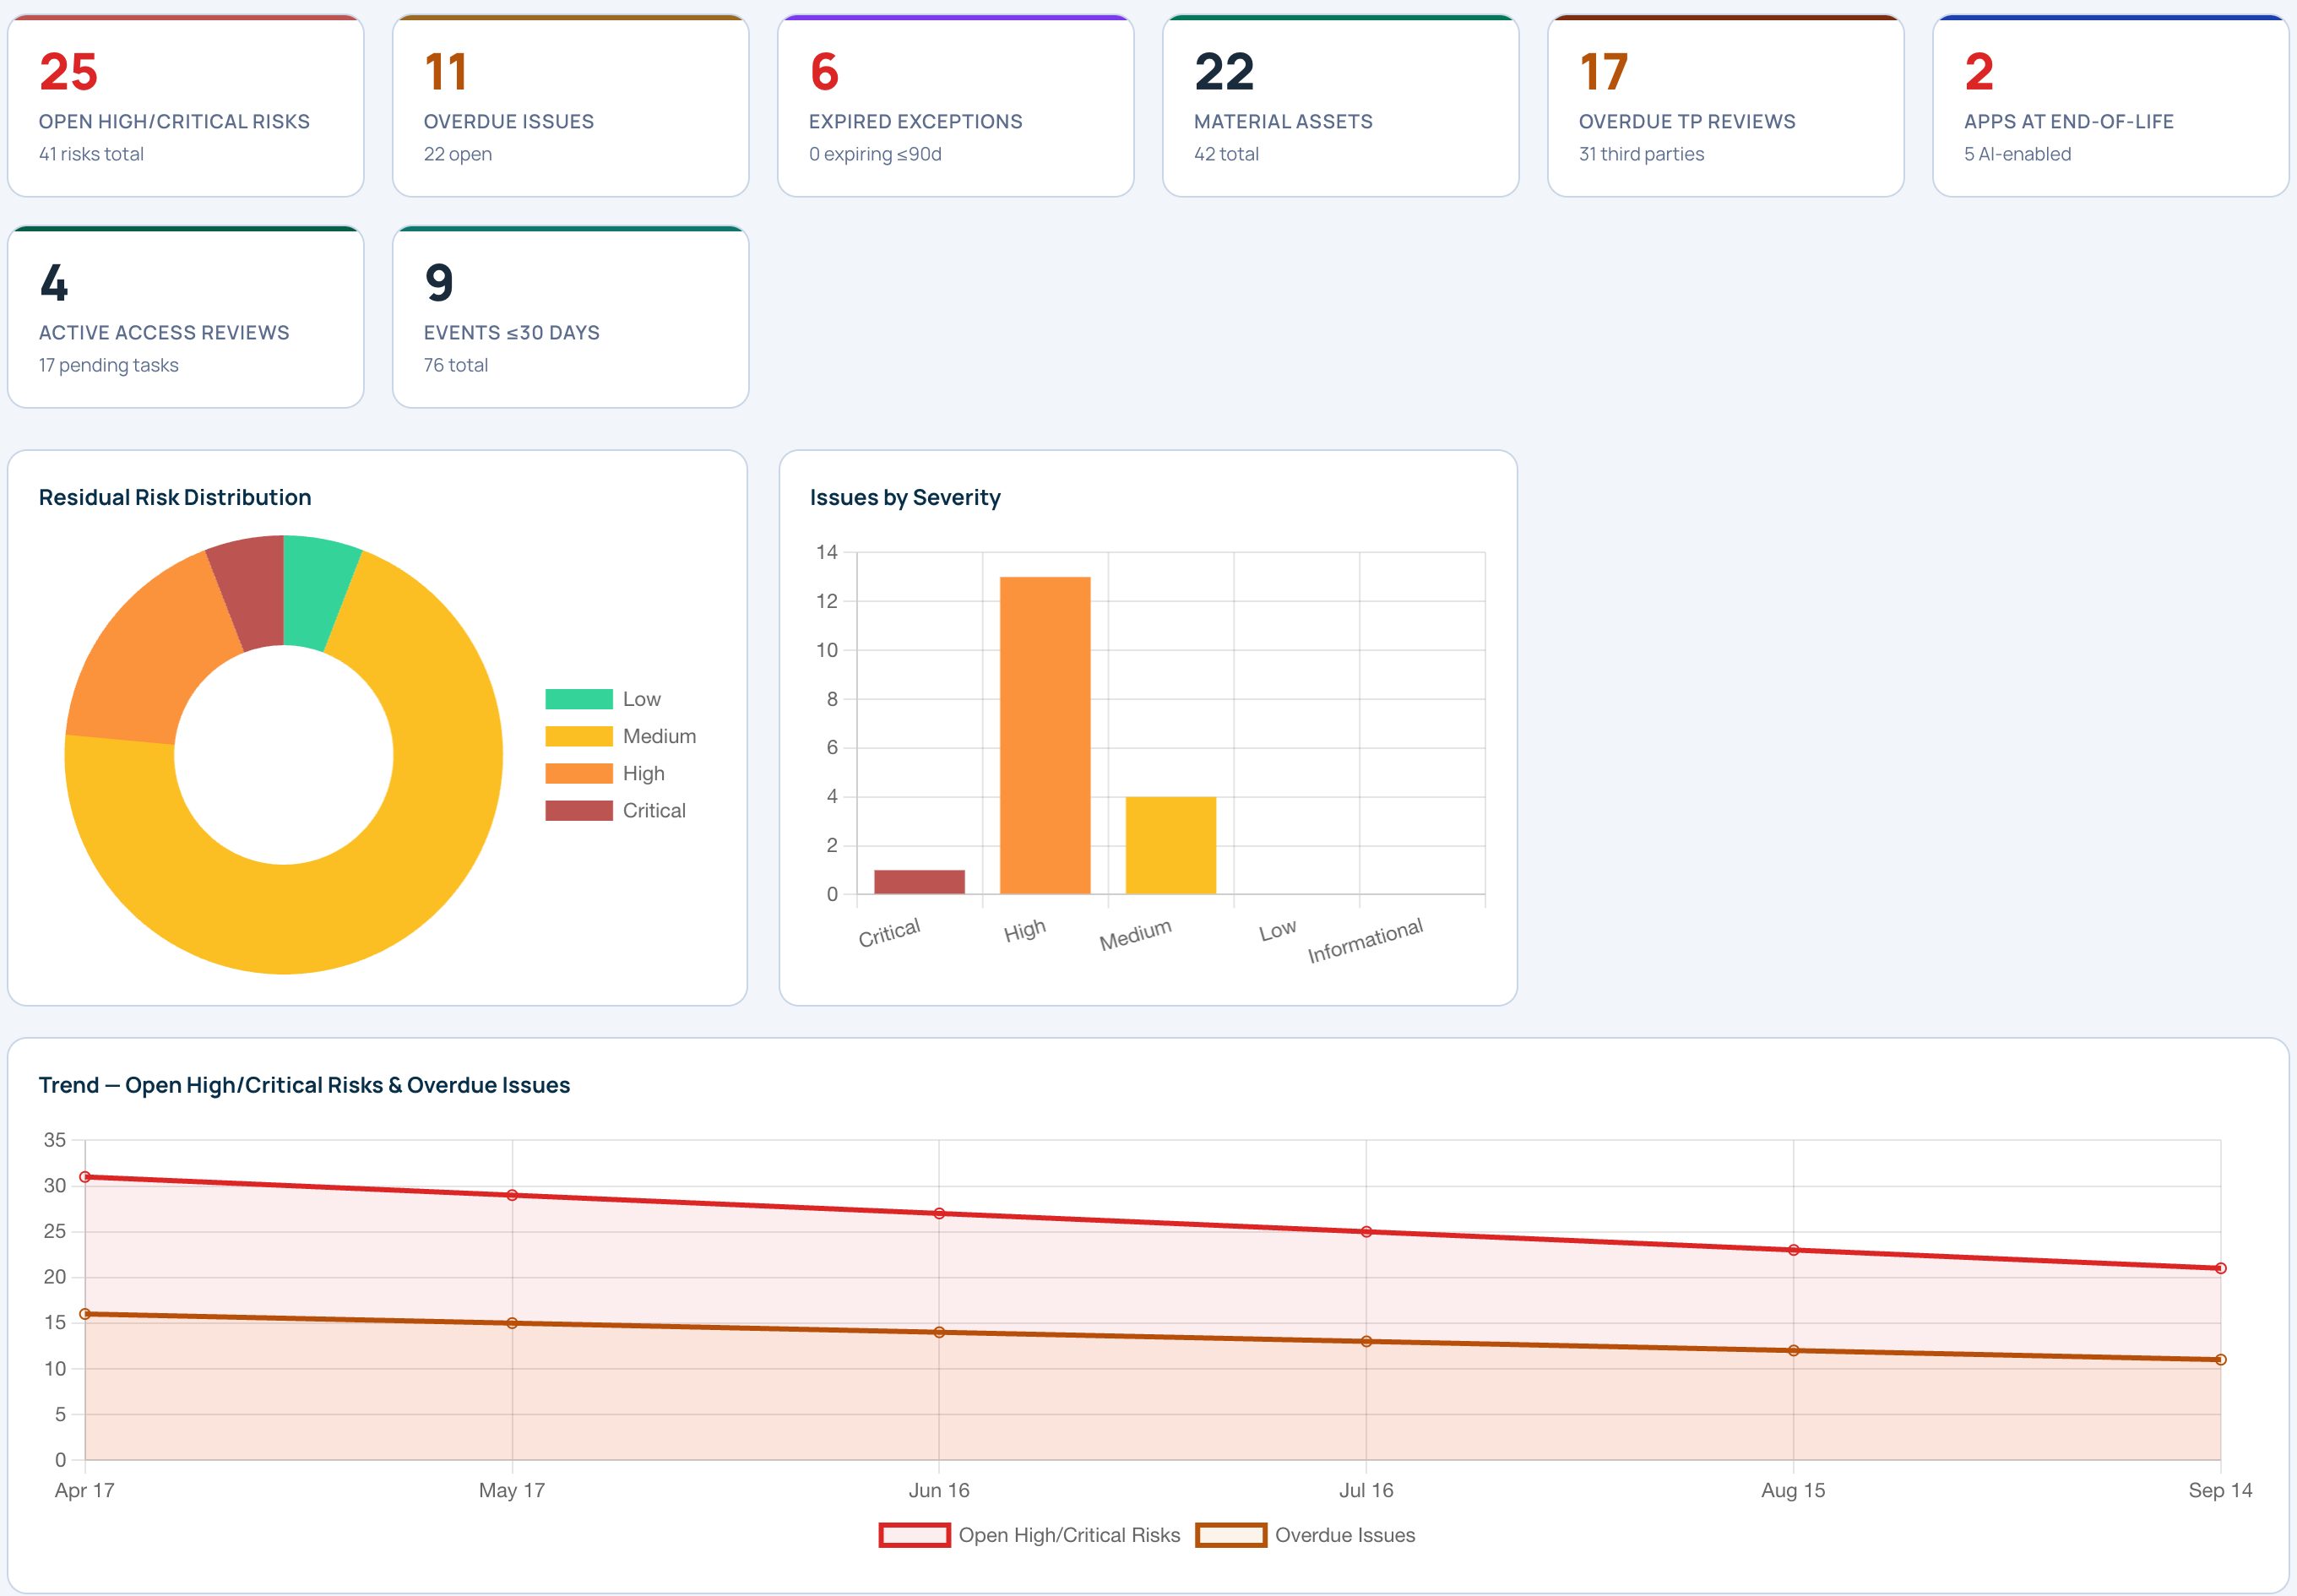
PS-01Policies & standardsHG-01How-to guidesAG-01AI governanceExecutive reporting reads from live records, not slides rebuilt the night before, and snapshots show how every number has moved.

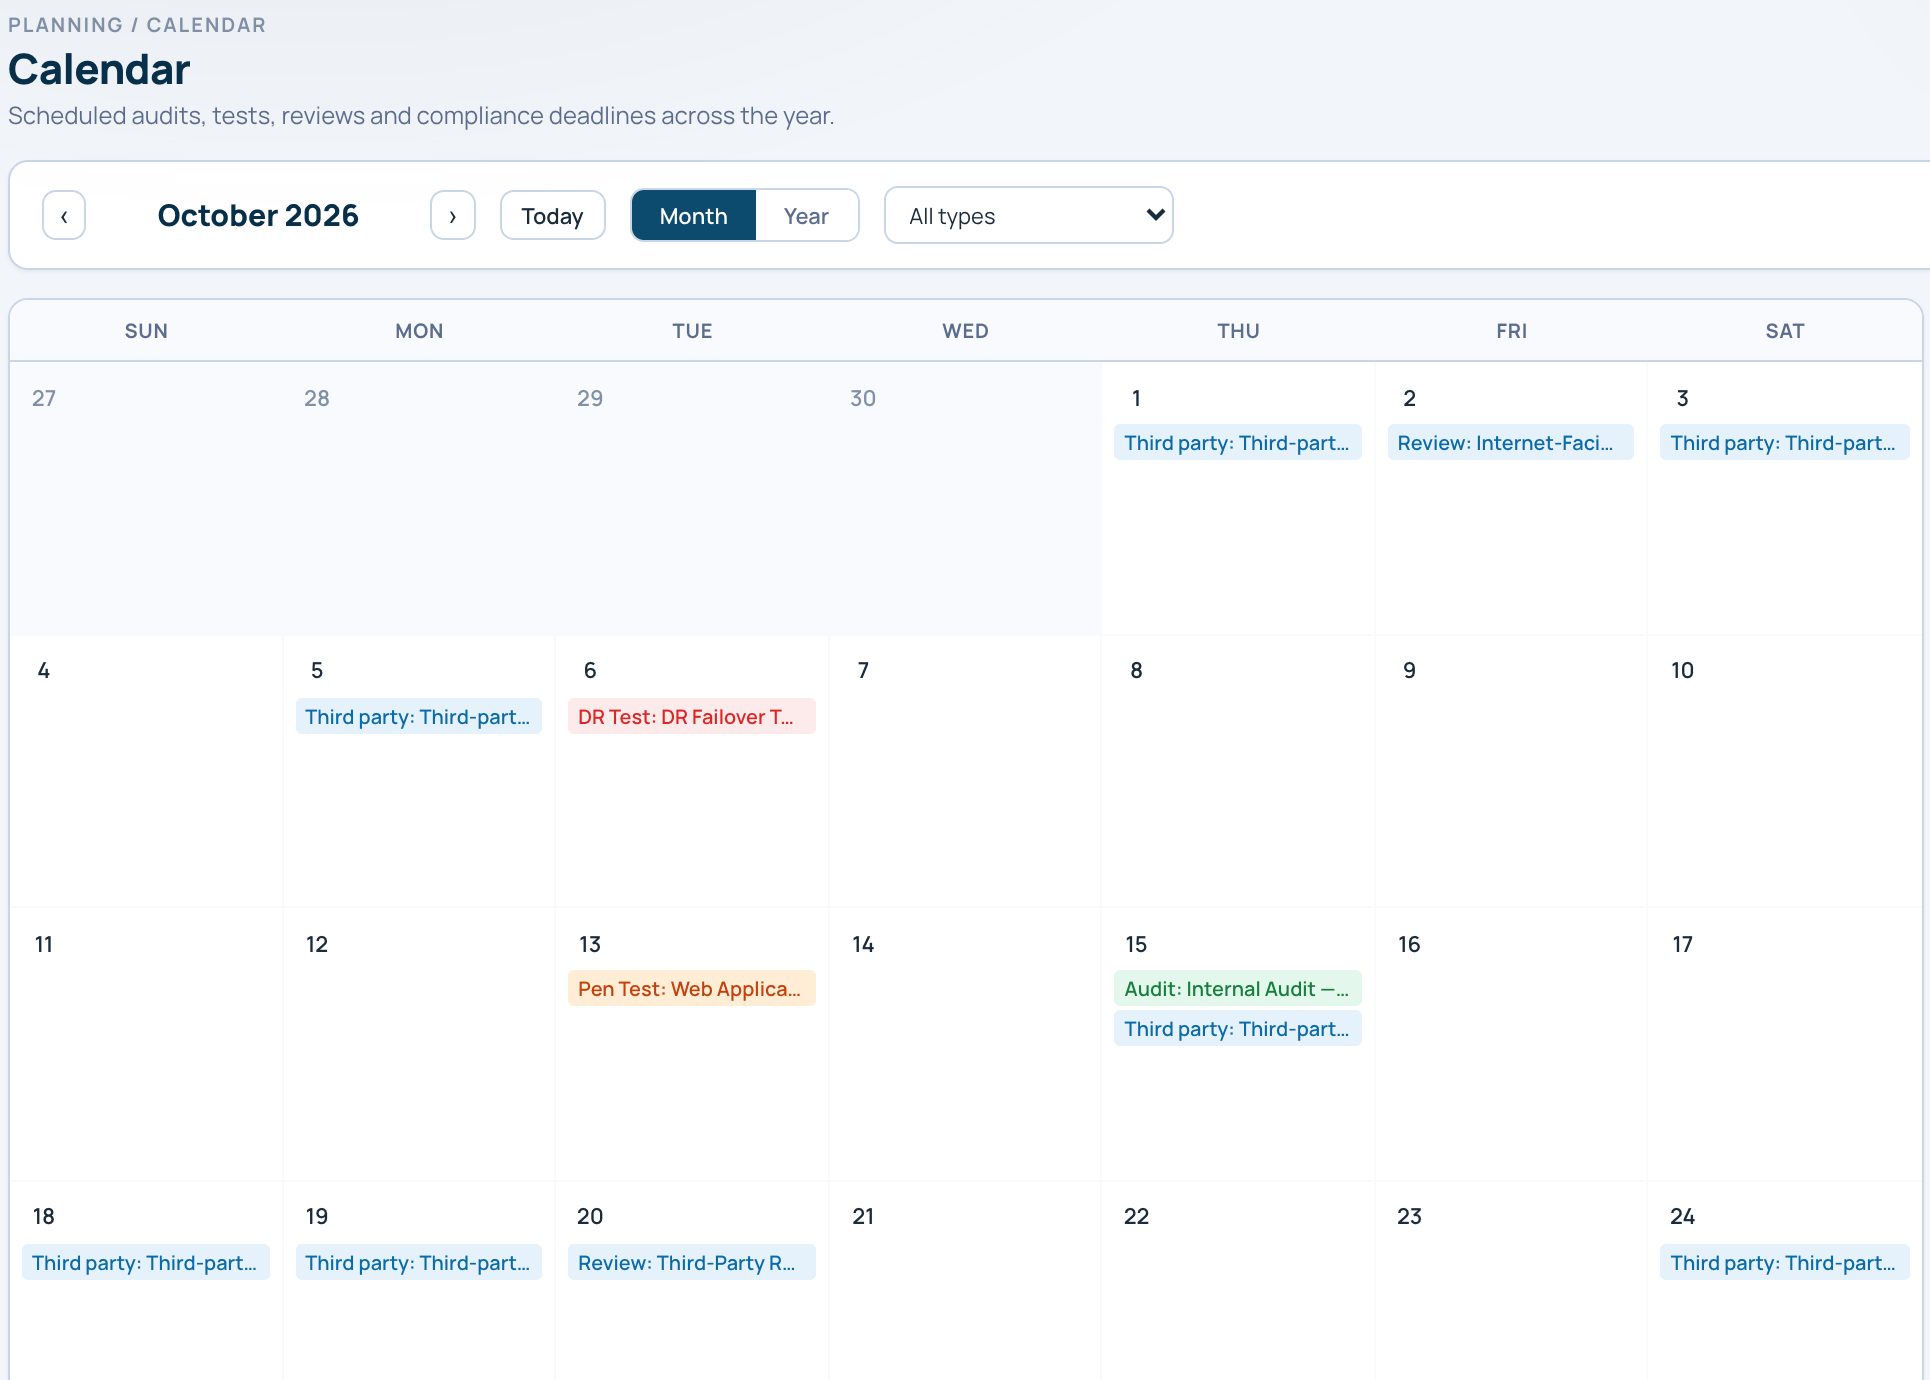
MT-01Security metricsBP-01Board packSA-01Search & AI assistantDay-to-day work runs in the same place as the risk it changes, so nothing moves without the right person seeing it.

WF-01Tasks & approvalsCL-01Compliance calendarMB-01MobileAD-01AdministrationWhy one platform
Every board pack is frozen when it is generated. The figure the board saw is the figure that stays on file.
Residual threshold, coverage window and review lead time are set per organisation, and the pack measures against them.
A short summary above the numbers (signal, impact, ask), so a director reads the point before the chart.
Ask the report a question in plain language and get an answer drawn from the risks, controls and evidence behind it.
Prove a control once and see conformance per framework, without re-testing it for every auditor.
Every figure opens the register row behind it, read-only for executives.
Request early access
We're onboarding a small group of pilot partners — regulated entities and agencies who want their governance to be one live record, not a reconstruction. Tell us who you are.
We'll only use your details to contact you about pilot access. No password needed yet — we'll set that up together once you're approved.
Thanks — your request is in the queue. We'll reach out once your access is approved.